Swiss vs German Email Privacy: Which Jurisdiction Is Safer?
Neither Switzerland nor Germany is a clear winner for email privacy. Germany has the stricter rulebook against profiling, Switzerland sits outside the EU and Fourteen Eyes, and both can order IP logging for a specific account while debating new retention powers.

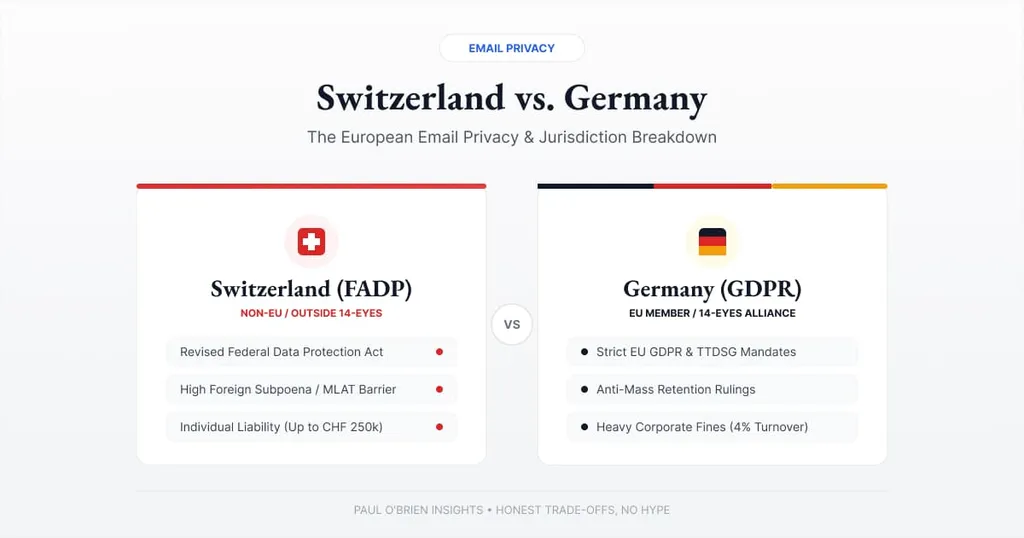
Neither Switzerland nor Germany is a clear winner for email privacy. Germany, under EU law, has the stricter rulebook against commercial profiling. Switzerland sits outside the EU and the Fourteen Eyes, which helps against foreign requests. Both can compel a provider to log an IP address for a specific account, and both are currently debating new retention powers.
When choosing a privacy-focused email provider, most people look at encryption or the interface. The more important security boundary is often jurisdiction. Two European countries dominate the privacy-first email landscape: Switzerland, home to Proton Mail, and Germany, home to Tuta and Mailbox.org. Both are marketed as privacy havens compared with US ad-funded webmail, but their legal frameworks work differently. Swiss branding also doesn’t guarantee good practice: see my Swissmail.org review for the red flags I found.
Short answer: choose Germany (or another EU provider) if your main worry is commercial profiling and you want GDPR’s enforcement behind you. Choose Switzerland if your main worry is foreign state requests. If you face a targeted investigation, neither jurisdiction protects you on its own, so encryption, metadata habits and the provider’s own design matter more. I’m not a lawyer, and this is a general overview, not legal advice.
At a Glance: Which Jurisdiction Suits Which Concern?
| User Profile | Best Fit? | Core Value Drivers / Key Trade-offs |
|---|---|---|
| Worried about advertising, tracking and data monetisation | Germany: Ideal | GDPR consent rules and corporate fines of up to 4% of global turnover. EU judicial cooperation applies. |
| Worried about foreign government requests | Switzerland: Strong fit | Outside the EU and the Fourteen Eyes. Foreign requests normally go through Swiss legal channels, though rules are shifting. |
| Business needing GDPR compliance for customer data | Germany or another EU base: Strong fit | Simpler compliance story inside the EU. Check each provider’s data processing terms. |
| Targeted by a domestic investigation | Alternative needed | Both can order IP logging for a specific account. Use encryption plus network protection. See what Proton does and doesn’t protect. |
| Wants mail unreadable by the provider | Depends on the provider, not the country | Tuta encrypts end to end by default. Mailbox.org does not by default. |
1. Statutory Frameworks: FADP vs GDPR
| Aspect | Switzerland | Germany |
|---|---|---|
| Main data protection law | Federal Act on Data Protection (FADP), revised and in force since 1 September 2023 | EU GDPR, plus national law such as the TDDDG (formerly the TTDSG) |
| Consent | A general consent obligation applies only to high-risk profiling, so processing is generally allowed without consent if the principles are met | GDPR requires a lawful basis for processing, and national law adds consent rules for tracking technologies |
| Penalties | Fines of up to CHF 250,000, aimed at responsible individuals rather than companies | Up to €20 million or 4% of global annual turnover for the most serious breaches, aimed at companies |
| EU adequacy | The revision was designed to align with the GDPR | Directly bound by the GDPR |
The practical difference is who is on the hook. Under the FADP, the fine falls on the responsible person, which can be a strong deterrent for a small provider. Under the GDPR, the exposure is corporate and can be far larger. Those figures come from Adnovum’s comparison, so check the statutes for any decision that matters.
2. State Surveillance and Court-Ordered Logging
Switzerland
Switzerland is not part of the Five, Nine or Fourteen Eyes alliances, which gives some baseline protection against arbitrary foreign dragnet surveillance. But that is not the same as no surveillance. Tuta, a competitor of Proton, points out that Switzerland’s intelligence service monitors communications of non-Swiss persons and shares intelligence with other agencies. Swiss courts can also order surveillance under the BÜPF for serious crimes. Swiss providers can’t decrypt properly encrypted message bodies, but they can be compelled to log IP addresses or monitor metadata for specific accounts. Proton states this plainly: it stores no permanent IP logs by default, but it “may have to comply with Swiss court orders to log specific users”.
Germany
German providers must comply with legitimate domestic court orders for lawful interception. Germany’s constitutional court historically struck down indiscriminate retention mandates That has made Germany relatively resistant to passive bulk collection, but the position is under pressure. A government bill would require internet access providers to store the IP addresses they assign to customers for three months. According to the Bundestag’s report, the bill had its first reading on 24 June 2026 and a public hearing in the legal committee on 7 October 2026, where experts disagreed sharply on whether it is data retention and whether it is justified. The obligation falls on internet access providers rather than email hosts, so it does not directly force a mail provider to keep logs, but it shows the direction of travel. Germany is also a Fourteen Eyes member, according to the same Tuta source.
Both countries are changing
Know the limits: neither jurisdiction is static. Switzerland is consulting on a revision of its surveillance ordinance that would expand retention and require larger providers to identify users. In February 2026, 19 organisations wrote to the Swiss government to object, and I found no final decision. In August 2025, TechRadar reported that Proton was moving some infrastructure out of Switzerland, starting with Lumo, to Germany, and building facilities in Norway. Check the current position before you decide.
3. International Requests
The old story was simple: a foreign agency can’t demand data from a Swiss host directly and must go through a Swiss court under mutual legal assistance, while EU providers sit inside a faster judicial network. The EU side has changed. The e-Evidence Regulation (EU) 2023/1543 applies from 18 August 2026. According to Bird & Bird’s summary, it lets authorities in one member state send production and preservation orders directly to a service provider in another, bypassing traditional mutual legal assistance, and it extends to providers outside the EU that offer services to EU users. That means a Swiss provider serving EU customers may also be in scope. I haven’t verified how this interacts with Swiss law, so treat that as an open question.
Swiss providers still receive plenty of legal requests. Proton’s published 2025 figures, which I covered in Proton Mail vs Fastmail, show 9,301 orders, of which 988 were contested and 8,313 complied with. Orders are not the same as content handed over, because zero-access encryption limits what can be given up, but the volume shows that Swiss jurisdiction is not a wall.
4. Operational Comparison
| Regulatory aspect | Switzerland (e.g. Proton) | Germany (e.g. Tuta, Mailbox.org) |
|---|---|---|
| Main legislation | Revised FADP | EU GDPR, German TDDDG |
| Maximum penalty | CHF 250,000, aimed at individuals | €20M or 4% of global turnover, aimed at companies |
| Intelligence alliances | Not in the Fourteen Eyes | An EU member and a Fourteen Eyes participant |
| Foreign data requests | Normally via Swiss legal assistance. EU orders may reach providers serving EU users | EU judicial cooperation, including direct e-Evidence orders from August 2026 |
| Court-ordered logging | IP logging possible under a Swiss court order | Target-specific logging possible under a court order |
| Pending changes | Surveillance ordinance revision under debate | Three-month IP address retention bill in the Bundestag |
| Content protection | Depends on the provider | Depends on the provider |
What Jurisdiction Doesn’t Decide
How well your mail is encrypted depends on the provider, not the country:
| Provider | Base | Encryption by default | Full Review |
|---|---|---|---|
| Proton Mail | Switzerland | Zero-access storage, with end-to-end encryption between Proton users | Proton Mail review |
| Tuta | Germany | End-to-end encryption by default, with encrypted subjects. Mail to other providers is not end-to-end | Tuta review |
| Mailbox.org | Germany | Transport encryption. PGP and S/MIME are available but opt-in, and mail is not zero-access by default | Mailbox.org review |
If a provider can’t read your mail, a court order gets little content from them wherever they sit. If it can, the law of its country decides what it must hand over. For the vocabulary, see what zero-access encryption really means.
The Verdict: Jurisdiction Follows Threat Model
- Choose Germany (for example Tuta) if your main concern is corporate overreach and commercial profiling. GDPR gives the strictest regulatory shield against third-party ad tracking and illegal retention, with corporate fines to back it. The trade-off is that EU judicial cooperation is getting faster, not slower.
- Choose Switzerland (for example Proton) if your threat model centres on foreign state requests and non-EU neutrality. Sitting outside the Fourteen Eyes and the EU framework is a real barrier. The trade-off is that Swiss courts can still order targeted IP logging, and the surveillance rules are being reconsidered.
- If you face a serious, targeted threat, pick the provider and encryption design first, and treat the country as a secondary factor.
Whichever you choose, both remain far better than ad-financed webmail that trades network-level tracking for a “free” inbox. I discuss that trade-off in free vs paid email: what you really pay with.
Frequently Asked Questions
Is Switzerland safer than Germany for email privacy?
It depends on your threat model. Switzerland offers distance from the EU and the Fourteen Eyes. Germany offers GDPR enforcement. Neither stops a court-ordered request about a specific account.
Is Switzerland in the Fourteen Eyes?
No. Germany is, according to Tuta’s list. Not being in the alliance doesn’t mean Switzerland has no surveillance or intelligence cooperation.
Can Swiss or German email providers be forced to log my IP address?
Both can be ordered by a court to log specific users in criminal investigations. Proton says so explicitly. Using Tor or a VPN protects your IP address from the provider.
Is a German email provider protected by GDPR?
Yes, GDPR applies directly. It governs how providers handle your personal data, but it does not prevent lawful interception orders.
Does the Swiss surveillance law change affect Proton?
It is under discussion and I found no final decision. Proton has said it is moving some infrastructure out of Switzerland because of legal uncertainty, so keep an eye on developments.
Does jurisdiction matter if my email is end-to-end encrypted?
Less for message content, but it still affects metadata, IP logs and what the provider can be compelled to do.
Note: this article contains no affiliate links, and it is a general overview rather than legal advice. Sources: Adnovum: FADP vs GDPR (third-party); Tuta: Fourteen Eyes (a competitor’s page); Bundestag: IP address retention hearing; Statewatch; TechRadar; Bird & Bird: e-Evidence. Checked 9 October 2026.

