DMARC Explained: What Happens When Email Auth Fails
DMARC passes only when SPF or DKIM passes and aligns with your From domain. Here is what a DMARC fail means and how to fix it.

DMARC is the policy layer that sits on top of SPF and DKIM. It tells receiving mail servers what to do when a message claiming to be from your domain fails authentication, and it checks that the domain that passed SPF or DKIM is the same domain your recipient actually sees in the From line. Without it, SPF and DKIM can pass while a forged From address still reaches the inbox.
If you landed here because of a bounce that mentions a “DMARC policy”, or a report that says “DMARC fail”, the short version is that a message failed both SPF and DKIM alignment for the domain in its From address, and the domain owner has asked receivers to act on that. This guide explains what that means, how to read it, and how to roll DMARC out without breaking your own mail. Standards and sender rules were checked against the RFCs and the providers’ own pages on 8 October 2026.
Short answer: DMARC passes when SPF or DKIM passes and the domain that passed matches the From domain. Start at p=none with reports on, fix every legitimate sender you find, then move to quarantine and reject.
This is part of a series on email authentication. Start with how SPF, DKIM and DMARC work together, then read the individual guides to SPF and DKIM.
At a Glance: Who Needs DMARC (and What to Do)
| User Profile | Best Fit? | Core Value Drivers / Key Trade-offs |
|---|---|---|
| Business with its own domain that sends customer email | Ideal | Stops exact-domain spoofing and protects deliverability. Needs a careful rollout so legitimate mail is not blocked. |
| Anyone sending in bulk to Gmail, Yahoo or Outlook.com | Required | Major providers require a published DMARC policy for bulk senders. p=none meets the minimum. |
| Individual with a custom domain used for personal mail | Strong fit | A simple record gives visibility and protection. Low effort once SPF and DKIM are set. |
| Owner of a domain that sends no email | Strong fit | A strict policy stops criminals using it. Takes minutes to set up. |
| Someone who only uses a free Gmail or Outlook address | Not applicable | The provider manages DMARC for you. |
What a DMARC Failure Actually Means
A “DMARC fail” is not the same as an SPF or DKIM failure. It means that neither SPF nor DKIM produced a result that both passed and aligned with the domain in the From header. A message can pass SPF and still fail DMARC if the SPF check was for a different domain.
| What happened | DMARC result | Why |
|---|---|---|
| SPF passes for the From domain | Pass | SPF passed and aligned |
| DKIM passes with a signature from the From domain | Pass | DKIM passed and aligned |
| SPF passes, but for your email provider’s bounce domain, not yours | Fail, unless DKIM aligns | SPF passed but did not align |
| DKIM passes, but the signing domain is your vendor’s | Fail, unless SPF aligns | DKIM passed but did not align |
| SPF fails and the message has no DKIM signature | Fail | Nothing authenticated the From domain |
| A forwarded message breaks SPF, and DKIM was altered in transit | Fail | Neither mechanism survived the hop |
Why SPF and DKIM Are Not Enough on Their Own
SPF confirms that a server was allowed to send for a domain, but it checks the hidden envelope sender, not the From address people read. DKIM confirms the message was not altered and was signed by a domain, but that domain does not have to be the visible sender. Neither says what a receiver should do after a failure, so enforcement was optional. DMARC closes both gaps with two ideas: alignment and policy.
1. Alignment: tying the checks to what users see
DMARC requires the domain that passed SPF or DKIM to match the domain in the From header. There are two modes, controlled by the aspf and adkim tags, and both default to relaxed.
| Mode | Rule | Example |
|---|---|---|
| Relaxed (default) | The domains share the same organisational domain | mail.example.com aligns with example.com |
| Strict | The domains must be identical | mail.example.com does not align with example.com |
2. Policy: telling receivers how to handle failures
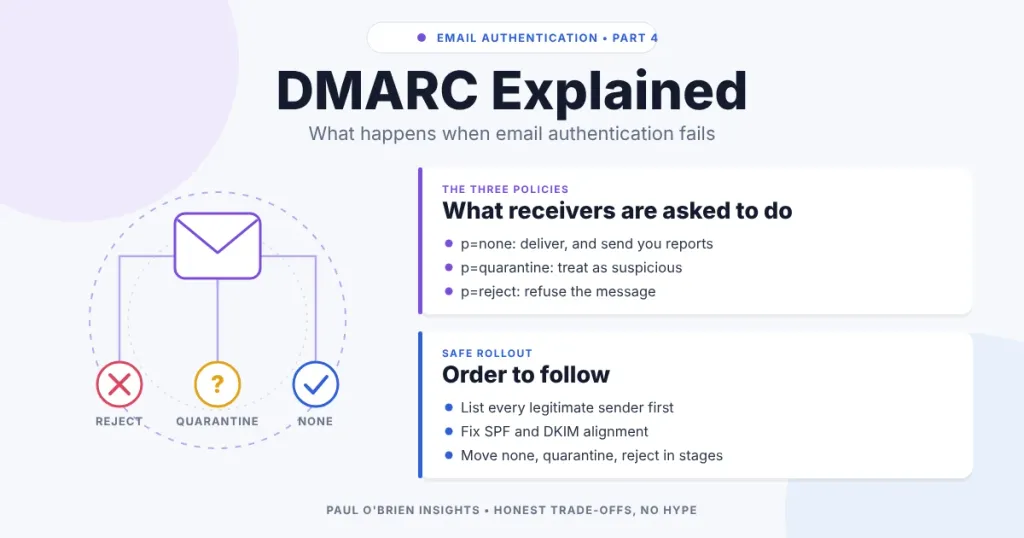
The domain owner publishes one of three policies for mail that fails DMARC:
| Policy | Mode | What receivers are asked to do | Use it when |
|---|---|---|---|
p=none | Monitoring | Deliver normally, and send reports | You are starting out and finding every legitimate sender |
p=quarantine | Suspicion | Treat as suspicious, typically sending it to spam | Reports are clean but you want a safety net |
p=reject | Enforcement | Refuse the message | All legitimate mail aligns and you want full protection |
The policy is a request, not a command. Receivers can and do apply their own judgement, so an enforced policy is strong protection but not a guarantee.
A DMARC Record Explained
A DMARC record is a DNS TXT record published at _dmarc.yourdomain.com. A typical starting record looks like this: v=DMARC1; p=none; rua=mailto:dmarc-reports@example.com.
| Tag | Meaning | Notes |
|---|---|---|
v | Version, always DMARC1 | Must come first |
p | Policy for the domain | none, quarantine or reject |
sp | Policy for existing subdomains | If absent, subdomains follow p |
np | Policy for non-existent subdomains | New in RFC 9989. If absent, sp or p applies |
rua | Where to send aggregate reports | A mailto: address |
ruf and fo | Failure reports, and when to send them | fo is ignored unless ruf is set |
adkim and aspf | Alignment mode for DKIM and SPF | r relaxed (default) or s strict |
t | Test mode | New in RFC 9989. t=y applies the policy one level lower |
What changed in 2026: the DMARC standard was updated in May 2026. RFC 9989 replaces RFC 7489, and RFC 9990 and RFC 9991 cover aggregate and failure reporting. Existing v=DMARC1 records keep working. The pct tag for percentage rollouts is no longer part of the standard, so do not rely on it. Use a time-based rollout instead, and note that receivers adopt the new tags at different speeds.
Reporting: The Part Most People Ignore
The rua tag is what makes DMARC useful. Receivers send aggregate reports, usually one a day, that list the source IP addresses sending mail for your domain, how many messages each sent, and whether SPF, DKIM and alignment passed. Reports arrive as compressed XML attachments, so most people use a free or paid reporting service to read them. If you send the reports to an address on a different domain, that domain has to publish a DNS record authorising it, or receivers will not send them.
These reports are how you find the forgotten systems sending as you: the old marketing tool, the CRM, the invoicing app. For a free place to start on the DNS side, see my guide to Cloudflare’s free email security features, which covers DMARC reporting.
How to Roll Out DMARC Without Breaking Your Mail
- List every sender. Your mail provider, marketing and support tools, invoicing and any app that sends as your domain.
- Make SPF and DKIM work for each one. Each service should sign with a DKIM key for your domain, or send from a domain that aligns with it.
- Publish
p=nonewith anruaaddress. Leave it for a few weeks and read the reports. - Fix what the reports show. Anything legitimate that fails alignment needs a DKIM signature or an SPF change.
- Move to
p=quarantine. Watch for complaints and missing mail. You can uset=yas a test step if your receivers support it. - Move to
p=reject. Do this only once reports are clean. - Protect domains that never send. Publish an SPF record that authorises nothing, and a
p=rejectDMARC record.
Sender Requirements: Gmail, Yahoo and Outlook.com
Since 2024, the big mailbox providers have required DMARC from bulk senders. The rules below are as published and may change.
| Provider | Who it applies to | DMARC requirement | Other points |
|---|---|---|---|
| Google (Gmail) | Bulk senders, meaning more than 5,000 messages a day to personal Gmail, from 1 February 2024 | Publish DMARC, and the message must pass. p=none is acceptable. The From domain must align with SPF or DKIM | SPF and DKIM both required, one-click unsubscribe, spam rate under 0.3% |
| Yahoo | Bulk senders, enforced from February 2024. Yahoo’s page does not define a volume threshold | Publish at least p=none, with alignment | SPF and DKIM both required, one-click unsubscribe, spam rate under 0.3% |
| Outlook.com, Hotmail and Live | Senders of 5,000 or more messages a day, from 5 May 2025 | At least p=none, aligned with SPF or DKIM | Non-compliant bulk mail is rejected, reported as 550 5.7.15 |
Even if you send a handful of messages a day, the same authentication improves your chance of reaching the inbox. My guide to using your own email domain explains why a custom domain makes this worth doing.
Common Reasons Legitimate Mail Fails DMARC
| Cause | What you will see | Fix |
|---|---|---|
| A third-party service sends as your domain without a DKIM key for it | SPF passes for the vendor’s domain, DKIM signs with the vendor, DMARC fails | Set up the vendor’s custom DKIM for your domain |
| Forwarding | SPF fails because the forwarder’s IP is not in your record | Rely on DKIM, which usually survives forwarding |
| Mailing lists that add footers or change the subject | DKIM breaks because the content changed | Expect some failures. Receivers may use ARC to trust the original result |
| Strict alignment on a subdomain setup | Alignment fails between mail.example.com and example.com | Switch to relaxed alignment, or send from the aligned domain |
| A forgotten system, such as an old CRM | An unknown source IP appears in reports | Identify it, then authenticate it or retire it |
| An SPF record that is broken or over the lookup limit | SPF returns an error | Fix SPF. See my SPF guide |
How the Protocols Work Together
| Protocol | Operational role |
|---|---|
| SPF | Declares which servers may send mail for a domain |
| DKIM | Signs messages so that tampering can be detected |
| DMARC | Checks alignment with the visible From domain and publishes the action to take on failure |
What DMARC Does Not Do
DMARC protects your exact domain from being forged in the From line. It does not judge whether a message is wanted, safe or honest, it does not stop lookalike domains such as a different spelling of your name, and it does not replace spam filtering. A criminal using their own properly authenticated domain passes every check. Think of DMARC as strong protection for your identity, not a verdict on any individual message.
Frequently Asked Questions
What does “DMARC fail” mean?
It means the message did not pass SPF or DKIM in a way that aligns with the domain in its From header. The domain owner’s policy then decides whether the receiver delivers, quarantines or rejects it.
Why was my email rejected because of the sender’s DMARC policy?
The domain in the From address publishes p=reject or p=quarantine, and your message failed alignment. If you are the sender, find which service is sending as your domain without authenticating properly. If you are the recipient, ask the sender to fix their setup.
Do I need DMARC if I only send a little email?
It is not required for small senders, but a p=none record with reports costs almost nothing and gives you visibility. It also protects your domain from being forged.
Should I use p=none, quarantine or reject?
Start with none to collect reports, move to quarantine once legitimate mail aligns, and use reject when reports are clean. Staying at none forever meets the bulk-sender minimum but gives no protection.
What is the pct tag, and is it still used?
It applied a policy to a percentage of failing mail so you could ramp up gradually. The updated standard, RFC 9989, no longer includes it, although some receivers may still honour it. Use a time-based rollout instead.
Does DMARC stop phishing?
It stops phishing that forges your exact domain. It does not stop lookalike domains, compromised accounts or phishing from a criminal’s own authenticated domain.
Do I need DMARC on a domain that sends no email?
Yes, it is worth it. Publish an SPF record that authorises nothing and a p=reject DMARC record so nobody can use the domain to send mail that looks like yours.
The Bottom Line
DMARC turns SPF and DKIM from two separate checks into enforceable protection for the domain your recipients actually see. Start with monitoring, fix what the reports show, and tighten the policy in stages. Then your domain is harder to forge, and your own mail is more likely to arrive. For the full picture, read the series overview.
Sources: RFC 9989 (DMARC), RFC 9990 (aggregate reporting), Google email sender guidelines, Yahoo sender best practices, dmarcian on Microsoft’s requirements.
Note: This article contains no affiliate links. Standards and sender rules were checked on 8 October 2026 and may change.

