Nostr Mail (Nmail) Review: Decentralised Email Tested
Nostr Mail (Nmail) is an open-source webmail client that carries email over the Nostr protocol, so your identity is a key pair rather than an account. It’s fast and genuinely encrypted between Nostr users, but it leaks some metadata and the bridge to ordinary email weakens the story.

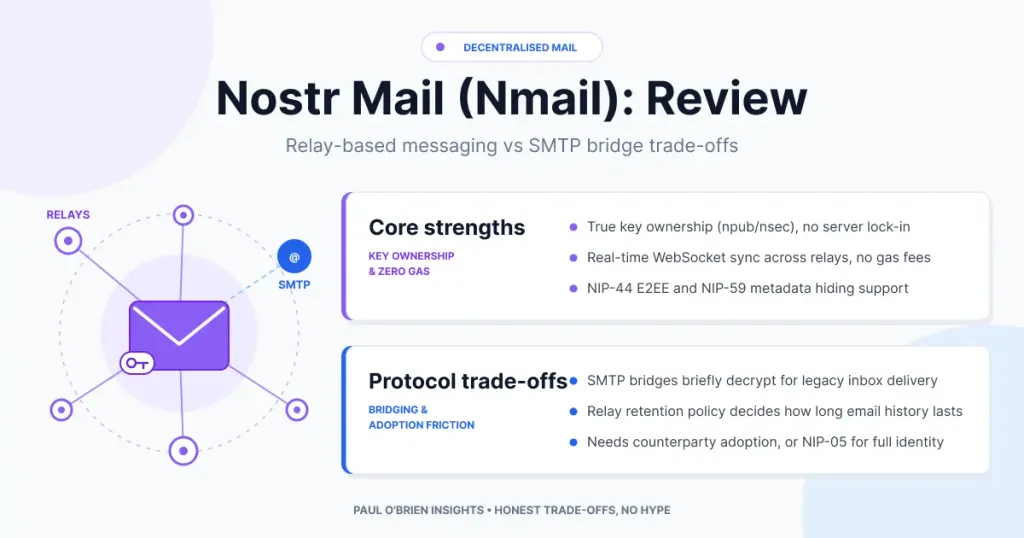
Nostr Mail (Nmail) is an open-source webmail client that carries email over the Nostr protocol, so your identity is a cryptographic key pair rather than an account with a provider. In my testing it was fast, and its encryption between Nostr users is real. But it asks you to manage your own keys, it still leaks some metadata, and the bridge to ordinary email weakens the privacy story.
Email has become run-of-the-mill. The same players control the space year on year: Google Workspace, Microsoft 365 and Fastmail. After experimenting with Mailflare and Agentic Inbox workflows alongside traditional mail, I wanted to look at decentralised email, and nostrmail.org was the obvious place to start.
Short answer: Nmail is a fascinating and usable experiment, not yet a replacement for a mainstream mailbox. It suits technically confident people who want key ownership and mostly talk to other Nostr users. It is a poor fit if you need to email ordinary inboxes privately, recover a lost password or rely on support.
At a Glance: Who Nostr Mail Is (and Isn’t) For
| User Profile | Best Fit? | Core Value Drivers / Key Trade-offs |
|---|---|---|
| Privacy enthusiast who already uses Nostr | Strong fit | Your keys, your identity, content encrypted between Nostr users. You carry all the responsibility for key safety. |
| Curious technologist | Ideal | A fast, working example of relay-based messaging. Expect rough edges. |
| Someone who emails ordinary Gmail and Outlook users | Partial fit | Works through an SMTP bridge, which sees the message in the clear. |
| Business needing support, SLAs and recovery | Alternative needed | No account recovery. Lose the private key and the identity is gone. |
| Anyone needing strong metadata protection | Partial fit | Relays can still see who a message is addressed to and when. |
What Is Nostr Mail (Nmail)?
Nmail is an open-source web application that brings a traditional email interface, with an Inbox, Sent folder, Compose window and Drafts, to the Nostr protocol. Instead of storing your messages on a central mail server like Gmail or Fastmail, it connects to independent Nostr relays over WebSockets.
Instead of a username and password hosted by a tech company, your identity rests on a pair of cryptographic keys, shown in Nostr’s NIP-19 format:
| Key | Looks like | Think of it as | Share it? |
|---|---|---|---|
| npub (public key) | Starts with npub1… | Your public address. It is how others find you and send you encrypted messages | Yes |
| nsec (private key) | Starts with nsec1… | Your master password and signature in one. Stored locally or in a browser extension, it signs messages and decrypts mail | Never |
When you write an email in Nmail it is signed locally with your private key, encrypted on your device and sent to the Nostr network. To the user it feels like webmail. Under the bonnet it is an end-to-end encrypted, relay-based messaging client where you hold the keys. (For how this differs from “zero-knowledge” and “zero-access”, see my guide to zero-access encryption.)
Speed and Responsiveness
Coming from bloated traditional webmail, the immediate takeaway is how snappy Nmail feels.
- Few page reloads. The interface loads once in the browser and manages state locally, so switching between Inbox, Sent, Drafts and Settings feels instant.
- Live syncing across relays. Rather than polling a central server, the client keeps WebSocket connections open to several independent relays, so new encrypted messages show up almost immediately.
- Decoupled architecture. Fetching from distributed relays and rendering the interface are separate jobs, which made browsing threads smoother than in corporate webmail suites.
This is my experience of using it, not a benchmark, and a busy mailbox with years of mail would be a better test than mine.
Beyond the Browser: Desktop and Mobile
Testing in a browser works well for a quick evaluation, but relying on webmail running third-party JavaScript isn’t the only option. Because Nostr is an open protocol, your data isn’t locked inside one web app. I haven’t independently verified every client below, so check each one before you trust it with your key.
- Native desktop app. A desktop client built with Tauri and Rust that caches your inbox in a local SQLite database, so you can draft and search offline and decrypt on your own machine.
- Progressive web app. You can turn nostrmail.org into a standalone desktop window from Safari or Chrome with the Add to Dock or Create Shortcut option. It gives you an isolated window with native notifications, but it is still the same web code.
- Mobile. Mobile Nmail clients exist as native ports. Because Nostr Mail builds on standard NIP-59 gift-wrapped events, other Nostr apps may be able to read the same encrypted events with your key. Whether they display them as sensible mail is something to test, not assume.
Is Nostr a Blockchain?
People hear “decentralised identity” and assume a heavy blockchain layer. Nostr Mail doesn’t use one:
- No global ledger or consensus. Nothing has to be mined or staked.
- No gas fees or tokens. You don’t pay network fees to send an email, save a draft or publish a NIP-05 profile.
- Cryptography plus lightweight relays. Nostr uses the same secp256k1 Schnorr signatures found in crypto networks to sign events. Relays simply store and pass along signed JSON events over WebSockets.
Security: What Is and Isn’t Protected
Nostr Mail overhauls email privacy in some ways, as long as you understand where the protection starts and stops.
Nostr to Nostr
When you email another npub or NIP-05 address, message content is encrypted on the client using NIP-44. According to the NIP-44 specification, version 2 uses secp256k1 ECDH, HKDF-SHA256, ChaCha20 and HMAC-SHA256, and was audited by Cure53 in December 2023. Messages are then sealed in NIP-59 gift wrapping, which hides the real sender inside the encrypted layers.
Be careful about what that means. Per the NIP-59 specification, the outer wrapper normally carries a tag naming the recipient so relays can route it. So a relay can typically see who a message is for, and roughly when, even though it can’t read the body, the subject or who sent it.
| What a relay can see | What stays hidden |
|---|---|
| That a gift-wrapped event exists, and its approximate time | The message body and subject |
| Normally, the recipient’s public key (for routing) | The real sender’s key, which sits inside the encrypted layers |
| Your IP address when you connect (per NIP-44’s own caveats) | Exact message length, which padding only partially obscures |
NIP-44 is also upfront about its limits: no forward secrecy, so a compromised key exposes past conversations, no post-quantum protection, and only partial hiding of message length.
The SMTP bridge: the legacy compromise
To reach Gmail or Outlook users, messages go through an SMTP bridge. Legacy servers can’t read Nostr events, so the bridge translates, which means it must decrypt the message before passing it onto the open internet. For that leg there is no end-to-end encryption, and you are trusting whoever runs the bridge. I couldn’t verify the operator of the bridge I saw, so I wouldn’t use it for anything sensitive.
Domain Ownership and NIP-05: the Decentralisation Paradox
NIP-05 maps a readable handle, such as paul@mydomain.co.uk, to a raw key. According to the NIP-05 specification, clients fetch /.well-known/nostr.json?name=… on the domain, which returns a JSON object mapping names to public keys in hex. Serving that file from a small Cloudflare Worker attaches your domain to your key without Google Workspace and without touching your MX records.
The key architectural point is that on centralised platforms your domain is your identity. If your domain host cancels your account or the domain is seized, your inbox goes with it. On Nostr your domain is a badge pinned to your public key, and the spec itself says NIP-05 is meant to identify a user, not verify them. If the domain disappears, the key stays your identity. See why using your own email domain makes sense for the conventional version of this argument.
Resilience: What if nostrmail.org Goes Offline?
The most compelling aspect is client independence. If the site vanished tomorrow you would lose that web interface, but your messages are encrypted events stored on independent relays. In principle you can open another client, or a native app, import your private key and your inbox reappears.
Two cautions. First, relays aren’t obliged to keep your events forever, and the specs suggest deleting messages after a time as a privacy measure, so a backup is wise. Second, that independence cuts both ways: losing your private key means losing the identity and the mail, and there is nobody to ask for a reset.
How Nostr Mail Compares
| Feature | Nostr Mail (Nmail) | Fastmail | Proton Mail |
|---|---|---|---|
| Identity | A key pair you hold | An account with the provider | An account with the provider |
| Encryption between users | End-to-end between Nostr users | Not end-to-end in its own apps | End-to-end between Proton users |
| Reaching ordinary inboxes | Through an SMTP bridge that sees the message | Native | Native, with optional encryption |
| Account recovery | None. Lose the key, lose the identity | Standard account recovery | Standard account recovery |
| Support | Community and open-source maintainers | Provider support | Provider support |
| Full Review | You are here | Fastmail review | Proton Mail review |
Pros and Cons
| Strengths | Weaknesses |
|---|---|
| You own your keys and your identity | No recovery if you lose the private key |
| Content encrypted between Nostr users, using an audited primitive | Recipient and timing metadata still visible to relays |
| Fast, responsive interface | No forward secrecy |
| Client independence: your data isn’t tied to one app | SMTP bridge decrypts mail for ordinary inboxes |
| No blockchain, tokens or fees | Young ecosystem, limited support and few users to write to |
Frequently Asked Questions
What is Nostr Mail?
An open-source way of sending email-style messages over the Nostr protocol, using encrypted events and public relays instead of a central mail server.
Is Nostr Mail private?
Message content is end-to-end encrypted between Nostr users. Relays can still see some metadata, such as the recipient and timing, and the bridge to ordinary email sees messages in the clear.
Is Nostr Mail a blockchain?
No. There is no ledger, mining or token. It uses signed events passed between relays.
What happens if I lose my nsec?
You lose access to the identity and its mail. There is no provider to reset it, so back it up carefully and never share it.
Can I email Gmail or Outlook users from Nostr Mail?
Yes, through an SMTP bridge. That leg is not end-to-end encrypted, because the bridge has to read the message to forward it.
Can I use my own domain?
Yes, with a NIP-05 file on your domain mapping a name to your public key. It doesn’t change your MX records or give you a conventional mailbox on that domain.
The Verdict
Nostr Mail shows that decentralised communication no longer has to sacrifice usability. The interface is fast and intuitive enough for daily experiments, and it gives you real ownership of your keys. For Nostr-to-Nostr messages it offers content protection and sender hiding that standard SMTP can’t match. I would not call it a replacement for a mainstream mailbox yet. Metadata, key recovery and the bridge are real trade-offs. For most people, a mainstream private provider is still the safer daily choice, with Nmail as something to try alongside.
Note: this article contains no affiliate links. Nostr Mail is young software, so check the current state of any client before trusting it with a private key. Sources: NIP-44; NIP-59; NIP-05; nostr_mail Dart package. Checked 9 October 2026.