QuickInbox.app Privacy Review: Claims vs the Code
QuickInbox.app promises anonymous, tracking-free disposable email. When I checked in October 2026, it loaded PostHog session replay, published no privacy policy or contact details, and tied paid plans to a bank card.

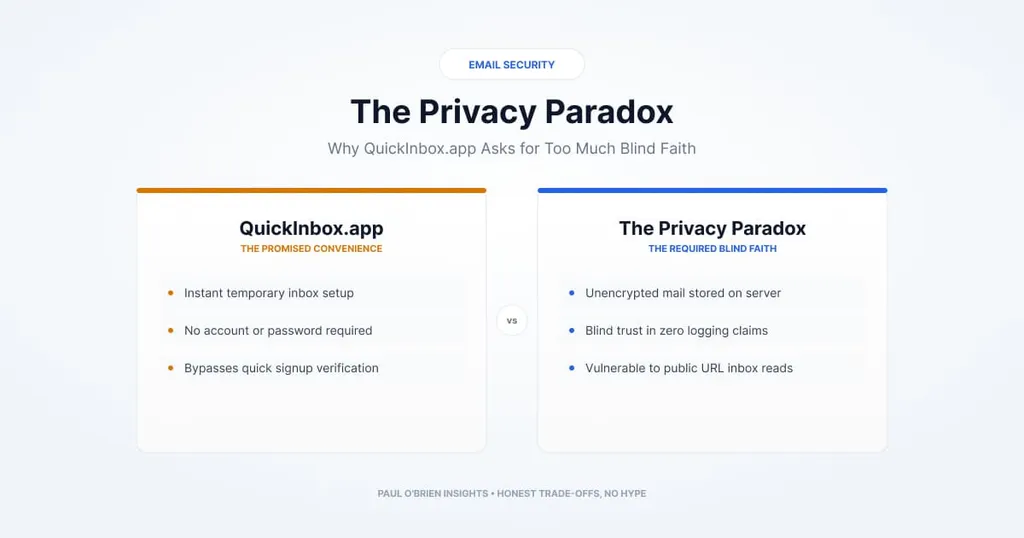
QuickInbox.app is a disposable email service that promises “No tracking” and “No identity leakage”. When I checked it in October 2026, its page loaded PostHog analytics with session replay, it published no privacy policy, terms or contact details, and its paid plans run through a card checkout. None of that proves bad faith, but it leaves users trusting a service they cannot check.
Short answer: treat QuickInbox.app with caution. Don’t use it for anything sensitive, such as a password reset or a one-time code, until the operator says who they are and what they log. This reflects the site as I found it in October 2026, and I will update it if that changes.
What QuickInbox.app Promises
The interface is clean and modern. Visitors get a free address that lasts 30 minutes, and paid plans extend that to 24 hours (€1), one month (€8) or a year (€80). Those prices are as I saw them in October 2026, and I have not re-checked them since. The marketing copy is confident:
- “Protect your privacy and send emails completely anonymously — free or paid.”
- “No personal data required • No tracking • No identity leakage”
A disposable inbox is meant to put a temporary address between you and sites that want to track you or add you to a mailing list. I compared how that differs from a forwarding alias in masked email vs disposable email. Here the question is narrower: does this particular service deserve the trust it asks for?
At a Glance: Claim vs What I Found
| Area | What the site says or implies | What I found (October 2026) | Why it matters |
|---|---|---|---|
| Tracking | “No tracking” | PostHog analytics loads on the first page view, with session replay configured | Behavioural data goes to a third party in the US |
| Consent | Nothing stated | No consent banner | Possible PECR and ePrivacy issue, depending on what the tool collects |
| Legal paperwork | Nothing stated | No privacy policy, terms or contact details | Users cannot learn what is logged, kept or shared |
| Operator | Anonymous | Domain via Cloudflare with redacted registrant details | Nobody identifiable to hold accountable |
| Build | Not mentioned | “Made with Emergent” badge and script | Not a fault in itself, but it adds an unexplained third party |
| Payment | “No identity leakage” | Paid plans use Stripe checkout | A card payment links a named cardholder to the purchase |
No Tracking, Except for the Tracking
The landing page says “No tracking”. The page source includes this (I have shortened it, and left out the project key):
posthog.init("phc_…", {
  api_host: "https://us.i.posthog.com",
  person_profiles: "identified_only",
  session_recording: { recordCrossOriginIframes: !0, capturePerformance: !1 }
})
This is PostHog, a product analytics platform. It loads on the first page view and sends data to PostHog’s US servers, and the session_recording block shows the site is set up for session replay, which records what visitors do on the page so it can be played back later. The recordCrossOriginIframes setting extends that to embedded frames.
To be fair, person_profiles: "identified_only" is PostHog’s recommended setting. According to PostHog’s documentation, it means events from anonymous visitors are stored without person properties, rather than being dropped. So the site is not building named profiles of anonymous visitors, but events still go to a third party, and “no tracking” is not an accurate description of that.
The consent question
I saw no consent banner. The UK rules have shifted recently, so I want to be careful here. Under PECR, storing or accessing information on a visitor’s device normally needs consent. The ICO’s updated guidance, reported by Brodies in May 2026, describes a statistical exception that removes the consent requirement for analytics used solely to see how a site is used, in aggregate. It excludes tracking or monitoring of users, and a third-party provider cannot use the data for its own purposes. Even then, the operator must give clear information and a simple way to opt out.
That leaves two problems for QuickInbox. First, session replay records individual visits, which is harder to fit within an exception about “how” a site is used rather than “who” is using it. That is my reading, not legal advice, and it would be for the ICO to decide. Second, the exception still depends on transparency, and this site offers no information and no opt-out at all.
Built With an AI App Builder
The source also shows how the site was made. It loads a script from assets.emergent.sh and carries a “Made with Emergent” badge in the bottom-right corner. That confirms it was built with Emergent.sh, an AI-assisted app-building platform.
Using a tool like this isn’t a problem in itself, and plenty of good products start that way. But it raises questions the site never answers. What third-party infrastructure sits between incoming mail and your screen? Who hosts it, and what does it log? There are small signs of haste too: a German label, “Am beliebtesten” (“Most popular”), sits on top of an otherwise English pricing table.
Going by what is visible from the outside, your data could reach at least three parties besides the operator:
| Third party | Role | What it can see |
|---|---|---|
| PostHog | Analytics and session replay | Page views, clicks, referrers, device details and approximate location from IP address |
| Emergent.sh | App-building platform | Unknown. The site does not say what runs on its infrastructure |
| Stripe | Payments (paid plans) | Cardholder and transaction details |
No Legal Paperwork at All
A disposable inbox handles personal data by design: IP addresses, email headers and the messages themselves. Under UK and EU GDPR, whoever runs the service is a data controller. Among other things, they have to tell users:
- who they are and how to contact them
- what data they collect, such as server logs, IP addresses and browser details
- why they collect it and on what legal basis
- how long messages and metadata are kept
- who they share data with, including any transfers outside the UK or EU
QuickInbox.app tells users none of this. I found no privacy policy in the footer, no terms of use and no email or postal address anywhere on the site. If you send a verification link or a password reset to one of these inboxes, you have no idea who can read it or how long it stays on their servers.
Who Runs It?
An RDAP lookup on the domain doesn’t help much:
"ldhName": "quickinbox.app"
"entities": [ registrar: "CloudFlare, Inc." ]
"nameservers": [ "coleman.ns.cloudflare.com", "oaklyn.ns.cloudflare.com" ]
The domain is registered through Cloudflare, which redacts the registrant’s details, and it uses Cloudflare’s nameservers. If traffic also goes through Cloudflare’s proxy, the origin server’s IP address is hidden too. The only contact the lookup returns is Cloudflare’s own abuse address.
Domain privacy is normal, and plenty of solo developers rightly use it. The problem is the combination. With a private domain, no contact details, no company name and no privacy contact, nobody can be held responsible. If something goes wrong, there is nobody to complain to and no regulator who would know where to start.
I also couldn’t tell whether similarly named domains, such as quickinbox.in, belong to the same operator. Disposable email services often spread across several domains so they are harder to block. Without official information, users cannot know which domains are run by whom.
Paying for Anonymity With Your Bank Card
The free 30-minute inbox needs no sign-up. The paid plans go through a Stripe checkout. Stripe is a respectable payment processor, but paying by card creates a record that links a real person to their purchase. Stripe keeps transaction records for regulatory reasons, and the operator receives payment details as well. Either can be required to hand over records through the proper legal process, so a paid “anonymous” inbox can be traced back to a named cardholder.
That isn’t a flaw unique to QuickInbox. Any privacy service that takes card payments has the same issue. Services that take it seriously say so plainly, explain what they keep, and often offer alternatives. QuickInbox does none of this while promising “no identity leakage”.
What a Trustworthy Provider Publishes
You can use this as a checklist for any disposable or alias service.
| Check | What good looks like | QuickInbox.app (October 2026) |
|---|---|---|
| Named company | Legal entity and address | None found |
| Privacy policy and terms | Linked from the footer | None found |
| Retention | Stated for messages and logs | Not stated |
| Third parties | Analytics, hosting and payments listed | Visible only in the page source |
| Consent and opt-out | Banner or clear opt-out for non-essential tracking | None seen |
| Contact route | Email or form for privacy requests | None found |
Frequently Asked Questions
Is QuickInbox.app a scam?
I have no evidence of that, and I am not accusing anyone of wrongdoing. The issue is a gap between the “no tracking” claims and what the page does, combined with no way of finding out who is responsible.
Does QuickInbox.app track you?
When I checked in October 2026, the page loaded PostHog analytics with session replay configured, which sends behavioural data to a third party. That is hard to square with “No tracking”.
Is a disposable email address anonymous?
Not automatically. The inbox may be anonymous to the website you give it to, but the operator can still see the messages, and your IP address and any card payment can identify you to them.
Is it safe to use for password resets?
I would not. Disposable inboxes can be public, expire quickly and may be read by the operator. For accounts you want to keep, a forwarding alias is a better fit. See masked email vs disposable email.
What are the alternatives?
Look for a named operator, a published privacy policy and ideally open-source code. Options include forwarding alias services and the aliases built into some mailboxes, such as DuckDuckGo Email Protection.
Does paying make a service more private?
Not by itself. A subscription can give a provider a reason to protect you rather than monetise you, but only if it is open about what it logs. I cover that trade-off in free vs paid email: what you really pay with.
Verdict: Privacy Needs Transparency
Anonymity and privacy aren’t the same thing. Anonymity means nobody knows who you are. Privacy means you have control over what happens to your data. A privacy tool can’t deliver the second if it won’t explain what it does with your data.
QuickInbox.app promises no tracking and then loads session-recording analytics. It publishes no privacy policy or terms, gives no way to contact the operator, and links paid accounts to real payment details without saying so. Until the operator publishes who they are, what they log and how long they keep it, treat the service with caution. Don’t use it for anything sensitive, and consider alternatives with a published privacy policy. If you only want to keep spam out, a password manager that creates aliases may be all you need.
Note: this post reflects QuickInbox.app as I found it in October 2026, and I will update it if the operator publishes a privacy policy or contact details. It contains no affiliate links. Sources: PostHog: anonymous vs identified events; Brodies: ICO storage and access technologies guidance (secondary source).

